
Explore Our Resources
Everything you need to optimize your technology investments
Pricing & Plans
Explore our transparent pricing models and find the perfect plan for your business needs and budget.
Access ResourceClient Success Stories
Real testimonials and case studies from businesses that have transformed their operations through our strategic technology partnerships.
Access ResourceBlog & Insights
Stay current with technology trends, industry insights, and expert perspectives on business transformation.
Access ResourceQuality of Technology Report
Learn about our comprehensive M&A technology due diligence assessments that protect your investments.
Access ResourceAI Transformation Services
Discover how artificial intelligence can transform your business operations and create competitive advantages.
Access ResourceQoT Due Diligence Checklist
Interactive technology due diligence checklist covering all 5 QoT pillars. Built for ETA searchers and SMB buyers.
Access ResourceTechnology DD Cost Estimator
Estimate first-year IT remediation costs by category. Know what to budget before you close on your acquisition.
Access Resource100-Day IT Integration Playbook
Week-by-week IT integration playbook for post-close. From Day 1 security lockdown to technology transformation.
Access ResourceFree IT & Cybersecurity Tools
Interactive tools to assess IT budgets, cyber risk, acquisition readiness, deal valuation impact, and insurance readiness.
Access ResourceFree Policy Templates
Read complete sample policies for AI, security and IT operations, then generate your own: policy choices start at suggested best-practice settings, and you answer the facts about your organization.
Access ResourceFree resource library
Every free guide, tool, policy template, checklist and report we publish, in one place. Filter by type or by your industry.
Type of resource
Industry
45 free resources
 GuideCMMC for North Carolina Defense Suppliers, in Plain EnglishCMMC in plain English for North Carolina defense suppliers and subcontractors: which level applies, what changed in 2026, what an SPRS score means and what to do first.
 GuideHow to Use AI at Work Safely: A Small Business GuideHow a small business can use AI tools safely: approve the right tools, keep sensitive data out, write a short policy, train people and have a person check the output.
 GuideEcoVadis and Customer Security Questionnaires: What US Manufacturers Need to KnowWhat EcoVadis ratings and customer questionnaires ask of US manufacturers, why customers ask, what EU law does and does not require, and which parts your IT can help prove.
 GuideRansomware: How North Carolina Small Businesses Prevent It and RecoverWhat ransomware is, how criminals usually get in, the handful of controls the FBI and CISA recommend, what to do in the first day, and whether to pay.
 GuideCyber Insurance for Small Businesses: What Insurers Ask and How to QualifyWhat cyber insurance covers, the security controls insurers commonly ask about, why claims get disputed, and how to get ready for your next renewal.
 GuideNorth Carolina Data Breach Notification Law: A Plain-English GuideWho North Carolina's breach notice law applies to, what counts as personal information and a breach, who you must notify and when, and the written disposal policy the law expects.
 Free toolSPRS Score CalculatorAnswer the 110 NIST SP 800-171 requirements in plain language and see your estimated SPRS score, from -203 to 110, plus the gaps worth the most points.
 Free toolCyber Insurance Readiness CheckerSixteen quick questions about the security controls insurers commonly ask about, with a readiness score and a fix list in priority order.
 Free toolCybersecurity AssessmentEighteen yes, partly or no questions on logins, computers, data and people, with a letter grade and the actions to take first.
 Free toolIT Budget CalculatorPick the IT services your business needs and get a realistic monthly and yearly budget range for your size.
 Free toolWebsite Health AnalyzerEnter any web address to check its speed, security settings and search basics, with a score for each.
 Free toolM&A Technology Readiness AssessmentFor buyers of a business: rate the target company’s technology risk and see how hidden IT costs could change the deal math.
 Free toolEmail Domain Security CheckerType your domain to see, in plain English, whether criminals can send email in your name and whether you meet the Google and Yahoo sender rules.
 Free toolMSP Evaluation ScorecardCompare up to three managed IT providers on the questions that matter, from response times to who owns your passwords, and print your results.
 Policy templateAI Governance PolicySet how your organization approves, uses, oversees and audits AI tools, aligned to the NIST AI Risk Management Framework.
 Policy templateAI Acceptable Use PolicyGive every employee clear, signable rules for using ChatGPT, Copilot, Gemini and other AI tools at work without exposing company or customer data.
 Policy templateIT Acceptable Use PolicySet clear rules for how employees use company computers, email, internet, software and data, and what monitoring they should expect.
 Policy templateInformation Security PolicyEstablish the core security program every insurer, auditor and customer now asks about: data classification, access control, patching, encryption, logging and vendor risk.
 Policy templateIncident Response PlanKnow exactly who does what in the first hours of a ransomware attack, data breach or business email compromise, including who to call and which notification clocks start.
 Policy templatePassword and MFA PolicyModern password and MFA rules based on current NIST SP 800-63B guidance: long passphrases, a password manager, no forced resets, and phishing-resistant MFA where it matters.
 Policy templateRemote Work and BYOD PolicyLet people work from home and use their own phones safely, with clear rules for home networks, device enrollment, company data and what happens when someone leaves.
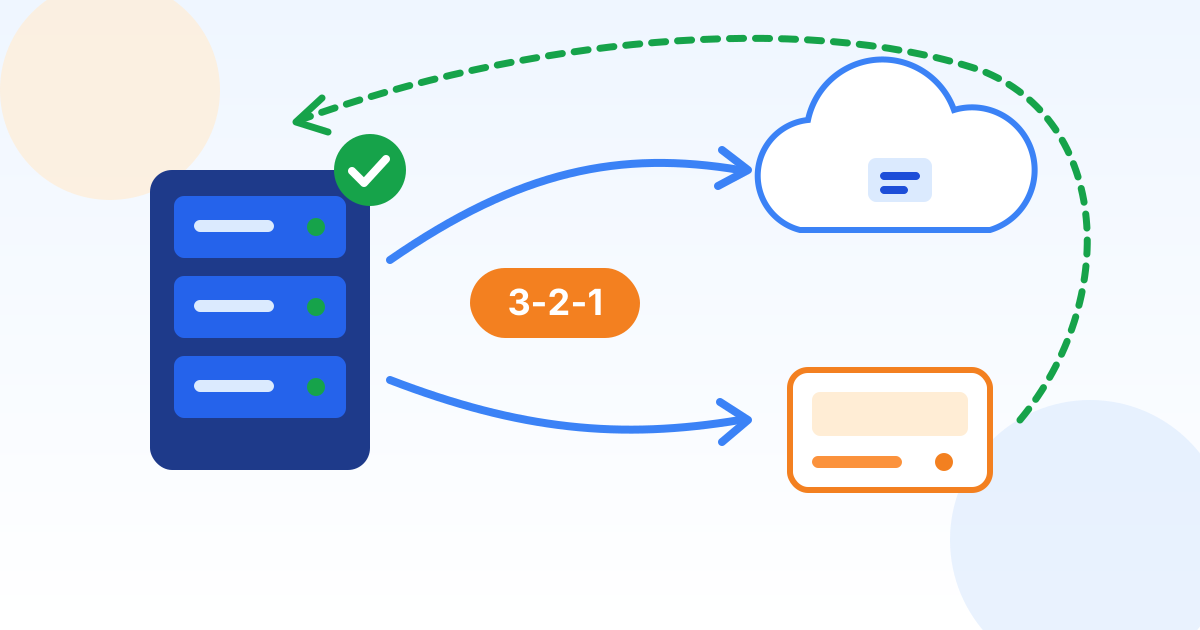 Policy templateData Backup and Recovery PolicyDefine what gets backed up, how often, where copies live and how fast you must recover, using the 3-2-1-1-0 rule that ransomware now demands.
 Policy templateWISP (FTC Safeguards Rule)A written information security program built for the FTC Safeguards Rule, for tax preparers, CPA firms, mortgage brokers, auto dealers that finance and other businesses the law treats as financial institutions.
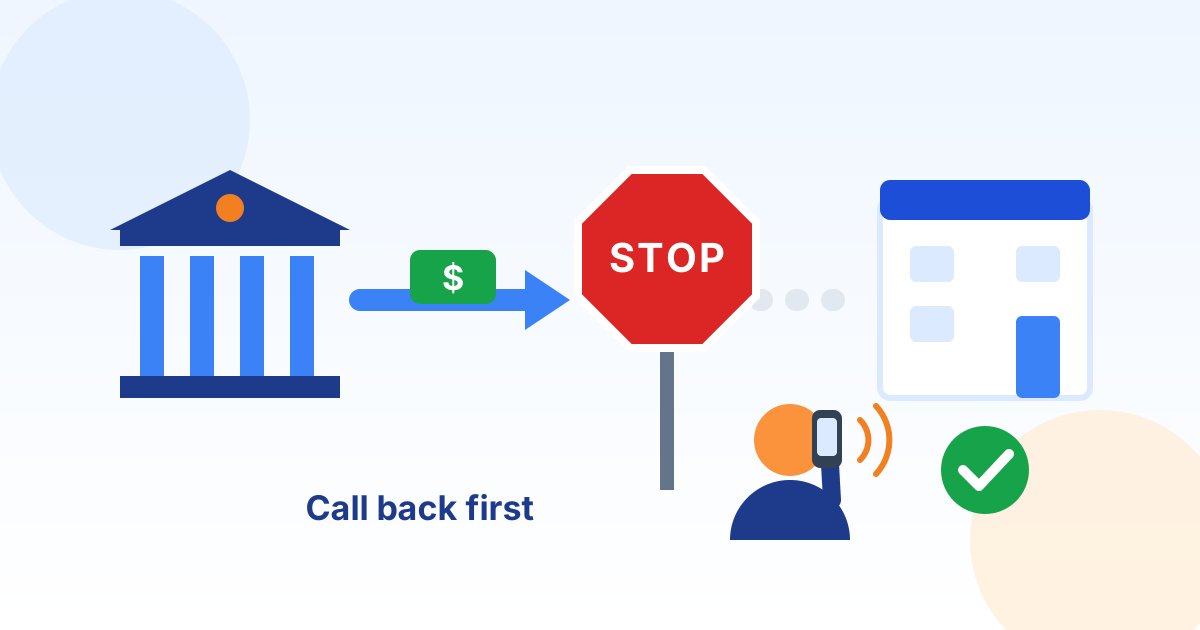 Policy templateWire Transfer Verification PolicyStop fake invoices and email payment fraud with simple rules: call back on a known number before any bank change, two approvers for large payments, and no payment changes by email alone.
 Policy templateVendor Risk Management PolicyChoose and monitor the vendors that hold your data or reach your systems: a vendor list, simple risk tiers, security questions, contract clauses, remote access rules and a clean exit.
 Policy templateAccess Control PolicyGive people only the access they need, protect every sign-in with MFA, keep admin accounts separate, review access every quarter and remove it the moment someone leaves.
 Policy templateData Retention and Destruction PolicyDecide what records to keep and for how long, with a sensible default schedule, legal holds, and secure destruction of paper and devices following NIST SP 800-88.
 Policy templateSecurity Awareness Training PolicyDecide who gets cybersecurity training, when, how phishing tests work, and which training records you keep for insurers and customer questionnaires.
 Policy templateBusiness Continuity PolicyKeep the business running through storms, outages, fires and cyberattacks: critical functions, recovery targets in plain words, a call tree and an annual tabletop test.
 Policy templateData Protection and Privacy PolicySet internal rules for the personal and confidential data you hold: collect less, limit access, share carefully with vendors, handle requests, and respond to a breach under North Carolina law.
 Policy templateIT Asset Disposal PolicyRetire old computers, phones, servers and copiers safely: track every device, wipe or destroy data to NIST SP 800-88, get certificates of destruction, and recycle through certified recyclers.
 Policy templateIT Supplier Code of ConductSet clear expectations for the companies you buy IT from: security, data protection, ethics, labor and environmental basics, take-back and recycling, and your right to ask for evidence.
 Policy templateSystem Security Plan (SSP) StarterA starter System Security Plan for defense contractors that handle CUI, organized by the 14 NIST SP 800-171 families, with a plan of action and milestones (POA&M) section and the CMMC rules that apply to it.
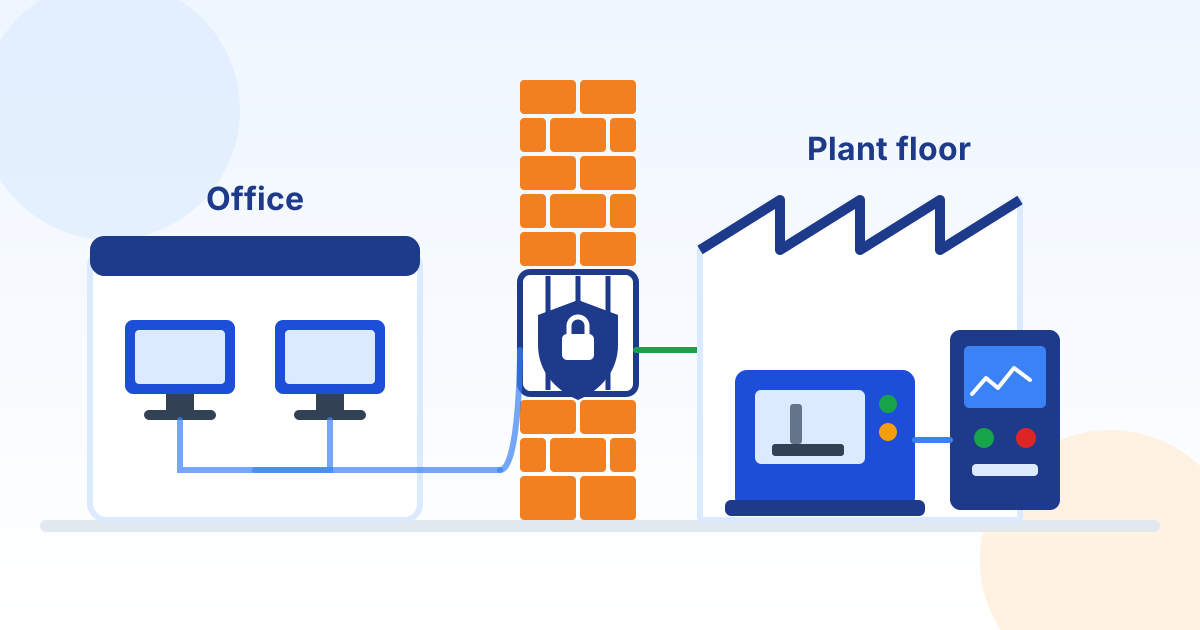 Policy templateOT and Plant Floor Security PolicyProtect the machines, PLCs, HMIs and plant PCs that run production: an equipment list, a wall between office and plant networks, safe vendor access, USB rules, backups of machine programs and a plan for machines you cannot patch.
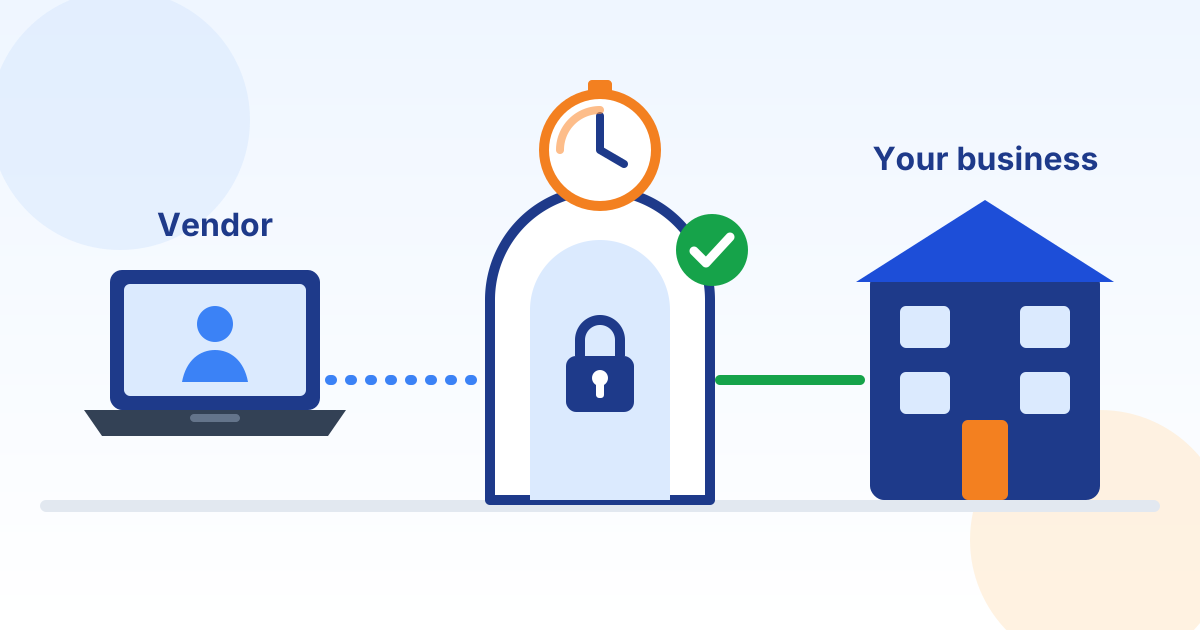 Policy templateVendor Remote Access PolicyControl how vendors, machine builders, software suppliers and IT providers connect in: approved tools only, a named account and MFA for every technician, access switched on per session, logged sessions and quick removal.
 Policy templateIncident Response PlaybooksStep-by-step playbooks for email account takeover, vendor or IT provider compromise, insider data theft, malware, misdirected data and website attacks, built to work with your incident response plan.
 Policy templateBreach Notification ProcedureDecide with your breach counsel whether an incident legally requires notice, then notify the right people with the right content: North Carolina rules by default, with HIPAA, FTC, DFARS and multistate steps when they apply.
 Policy templateIncident Report FormThe forms to fill in during a cyber incident: an initial report, triage sheet, timestamped log, evidence and chain of custody register, decision log, notification tracker, cost tracker and closure summary.
 Policy templateTabletop Exercise PlanRehearse your incident response plan in a two-hour guided discussion: ready-made ransomware, wire fraud and account takeover scenarios with timed injects, a scoring sheet and an after-action report.
 ChecklistRansomware: the first 24 hoursHour-by-hour steps for the first day after ransomware or a suspected breach: what to unplug, who to call, and what to report.
 ChecklistEmployee offboarding IT checklistEverything to revoke, recover and transfer when someone leaves: accounts, MFA, shared passwords, email, devices, keys and licenses.
 ChecklistOffice move IT checklistThe IT plan for moving or opening an office: internet orders, phones, cabling, Wi-Fi, cameras, cutover weekend and testing.
 ChecklistEcoVadis IT evidence checklistThe IT and data security documents to gather before an EcoVadis assessment or a large customer’s security questionnaire.
 ReportNorth Carolina Small Business Cyber Risk Report 2026The latest FBI and NC Department of Justice numbers on cybercrime in North Carolina, what they mean for a small business, and seven practical steps.
 ReferenceIT and Cybersecurity Glossary for Business OwnersPlain-English definitions of the IT, security, compliance and AI terms in vendor quotes, insurance forms and customer contracts, from MFA to CMMC.
Featured Resources
Popular guides and tools to accelerate your success
Need Personalized Guidance?
Our experts are ready to help you leverage technology for business success